Security and privacy
Capy is SOC 2 Type II compliant and doesn't train models on your non-public code or chats. Capy stores your threads in its cloud, including threads that run on your own device. New work is visible to everyone in your organization unless someone makes it private.
Compliance
| Item | Details |
|---|---|
| SOC 2 | Type II. Request the report from the Trust Center. |
| DPA | The Data Processing Addendum in the Terms of Service covers business customers when Capy processes personal data for them. For a separate agreement, book a call. |
| Model training | Capy doesn't use your non-public code, messages, files, or other content to train models that Capy develops or controls, unless you opt in or agree to it in writing. |
| Staff access | Capy staff access your content only to give support you ask for, when you give permission, or when security or the law requires it. Automated monitoring may also read threads so support can find and fix problems. |
| Zero data retention | Available by agreement for Capy's own storage on Enterprise plans. Book a call to discuss it. |
| Run in your own cloud | Available on Enterprise plans. Book a call to discuss it. |
| Data location | The United States and other countries where Capy and its subprocessors operate. The Subprocessors page lists each provider and its locations. |
| Egress IP addresses | Not published. Contact us for the list before you turn on an IP allow list, on GitHub or elsewhere. |
| Account data | Covered by the Privacy Policy. |
| Security reviews | Book a call for an enterprise security review. |
| Vulnerabilities | Email security@capy.ai. |
Model providers
On Capy credits, requests go to the model provider under Capy's agreement with that provider. The models table shows each model's zero data retention status on Capy credits. On your own API key or subscription, requests go under your agreement, including any zero data retention terms in it.
Some background requests, such as thread titles and pull request summaries, always run on Capy's provider accounts under zero data retention terms.
Settings → Models lets admins restrict a model to an organization key with Only, or turn off members' own keys. See Organization settings.
Your data
Capy stores this data:
- Threads. Messages, tool calls, and their output.
- Threads on your device. Your files stay on your disk, but anything the agent reads or prints goes into the transcript. Cloud checkpoints, on by default, keep a temporary copy of uncommitted work, following
.gitignore. You can turn them off in device settings. - Cloud machines. Each thread's machine is an isolated VM with your checkout, packages, and scratch files. Capy deletes a machine asleep for 14 days, with everything you didn't push or save to Drive.
- Drive files. Drive keeps files apart from machines, and keeps earlier versions for a limited time.
- Environment variables. Values are encrypted at rest.
Threads, files, and settings stay until you delete them.
Delete your data
- A thread. Delete is available in the thread's menu. Members can also delete a shared thread from the Threads page. Only the owner can delete a private thread or a Captain.
- An organization. Delete organization in organization settings is available only to owners. Deletion cancels paid subscriptions, stops running work, and removes the Slack and Linear connections.
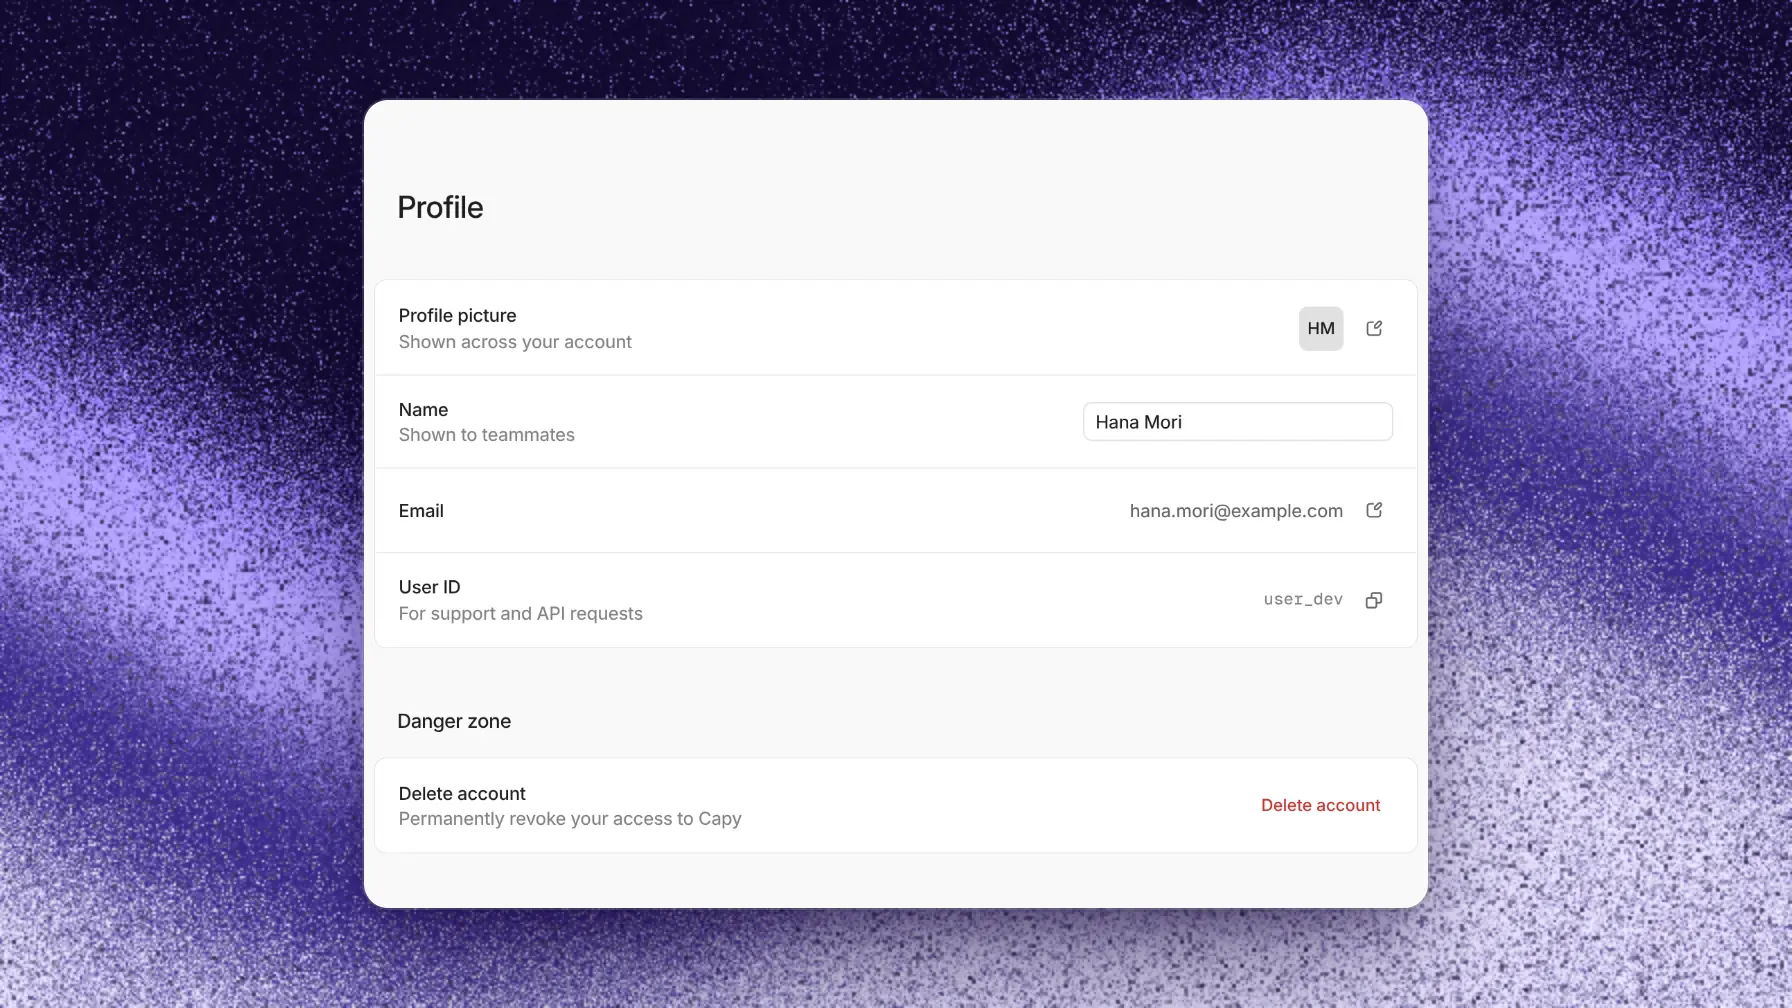
- Your account. Delete account in Settings → Profile removes your sign-in and revokes your API keys. Your threads stay in their organization.
Deleted data can be restored. On request, Capy permanently deletes it within 30 days. Email support@capy.ai to ask.
Visibility
New projects, threads, and Captains are visible to everyone at your organization unless you or your organization choose private. New folders start private. Anyone who can see an item can work in it: write in the thread, steer the Captain, or change the project's settings. Only the owner changes who can see it.
| Item | Shared | Private |
|---|---|---|
| Project | Everyone at the organization | The owner and the people they add. Admins see its name, owner, and size, but can't open it unless added. |
| Thread | Everyone who can see its project | The owner and the people they add |
| Captain | Everyone who can see its project | The owner and the people they add. Crew threads, reports, and drive follow the Captain. |
| Folder | Everyone at the organization | The owner and the people they add |
A private project limits everything in it, so a shared thread in a private project is visible only to the project's people. A folder's access covers only the folder's name and grouping. Each thread in it keeps its own access.
Make work private
Share on a thread or Captain supports Only specific people. In the composer, /private makes the thread or Captain private, and /shared shares it again. Projects have Share in their settings, and folders have Share folder. The people you add see everything the thread's agent sees, including your personal drive.
Sharing settings
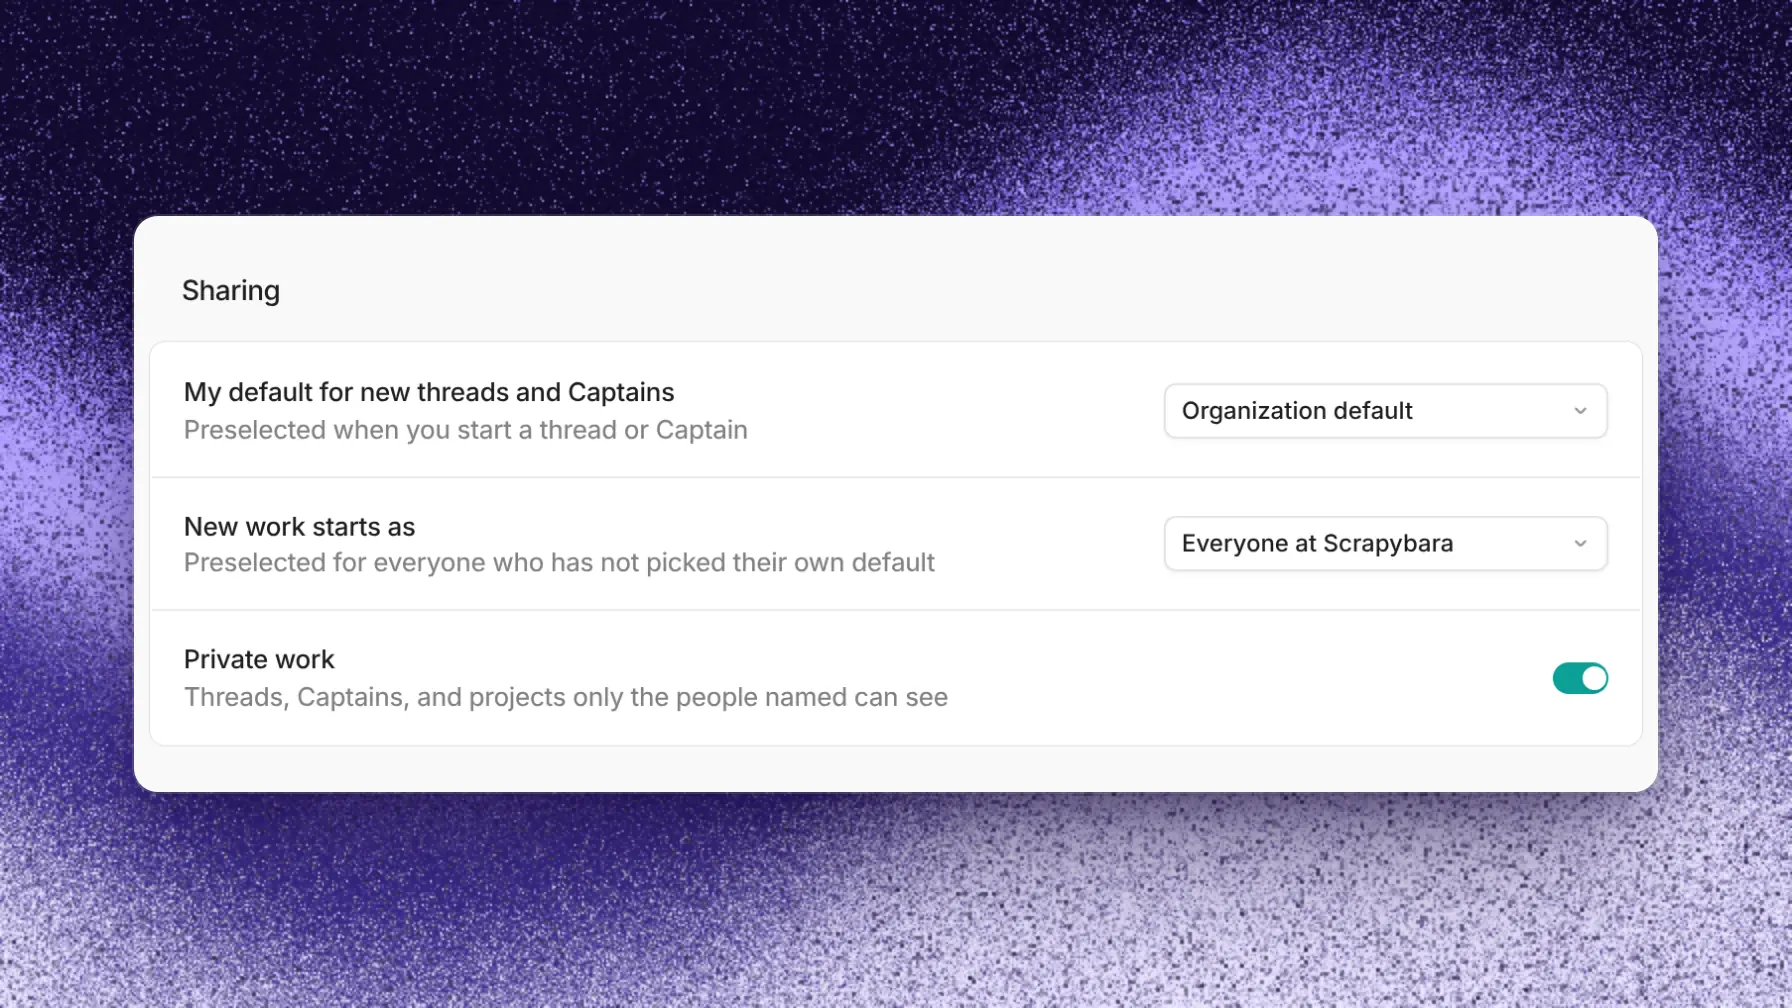
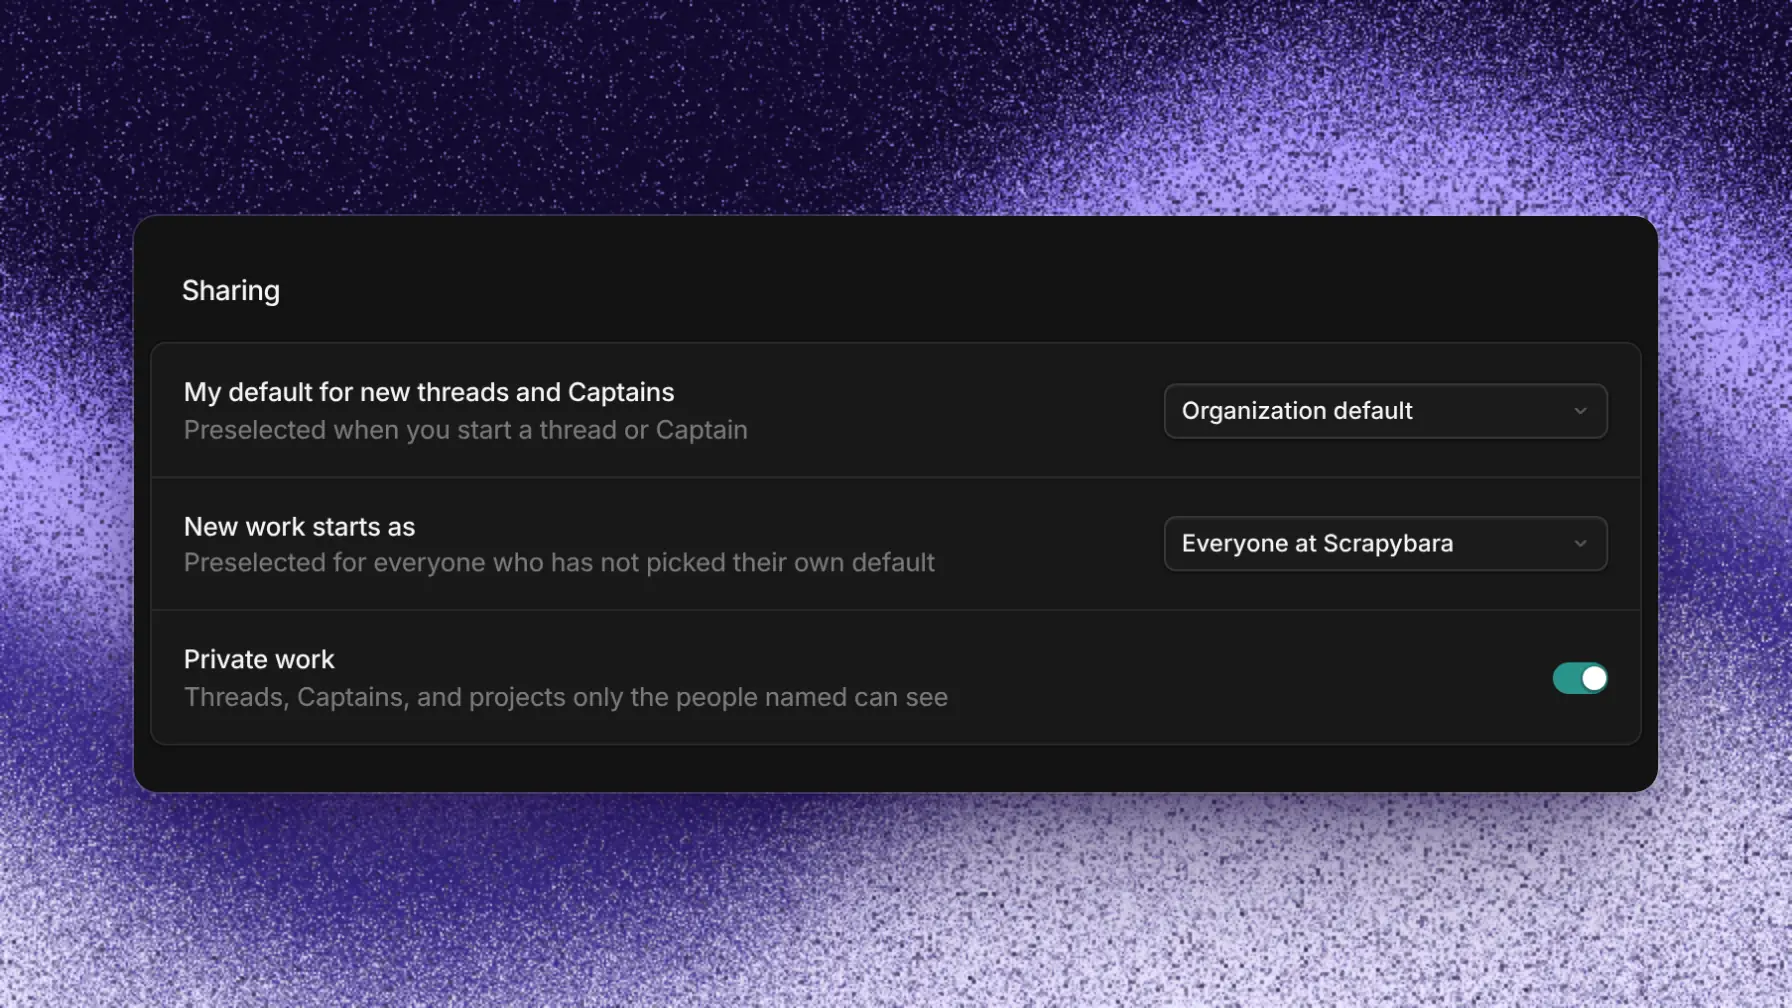
Admins control sharing in Settings → Organization → General. Private work, on by default, lets members make private threads, Captains, and projects. New work starts as sets the default access, and each member can override it with My default for new threads and Captains.
Drive, pull requests, and billing
| Drive | Who can see it |
|---|---|
| Organization | Every member |
| Project | Everyone who can see the project |
| Personal, Project + personal | Only you |
| Captain | Everyone who can see the Captain |
| Automation | Everyone who can see the automation's project |
A Drive share link has its own setting: the link's creator and admins, members who can see the drive, or anyone with the link.
The Pulls page shows every member the pull requests of every repository your GitHub App installation covers that any project uses, private projects included. A pull request's linked thread shows only to people who can see that thread. To keep a confidential repository's pull requests from colleagues, leave the repository out of the installation.
On the usage pages, admins and owners see private work they can't open: the owner, dates, credits, tokens, machine hours, and a private project's name. They don't see titles or content. Other members see one Private work entry per owner.
Single sign-on
Admins can have members on a verified domain sign in through Google Workspace, Okta, Microsoft Entra ID, or another SAML 2.0 identity provider, and can require it. See Single sign-on.
Devices
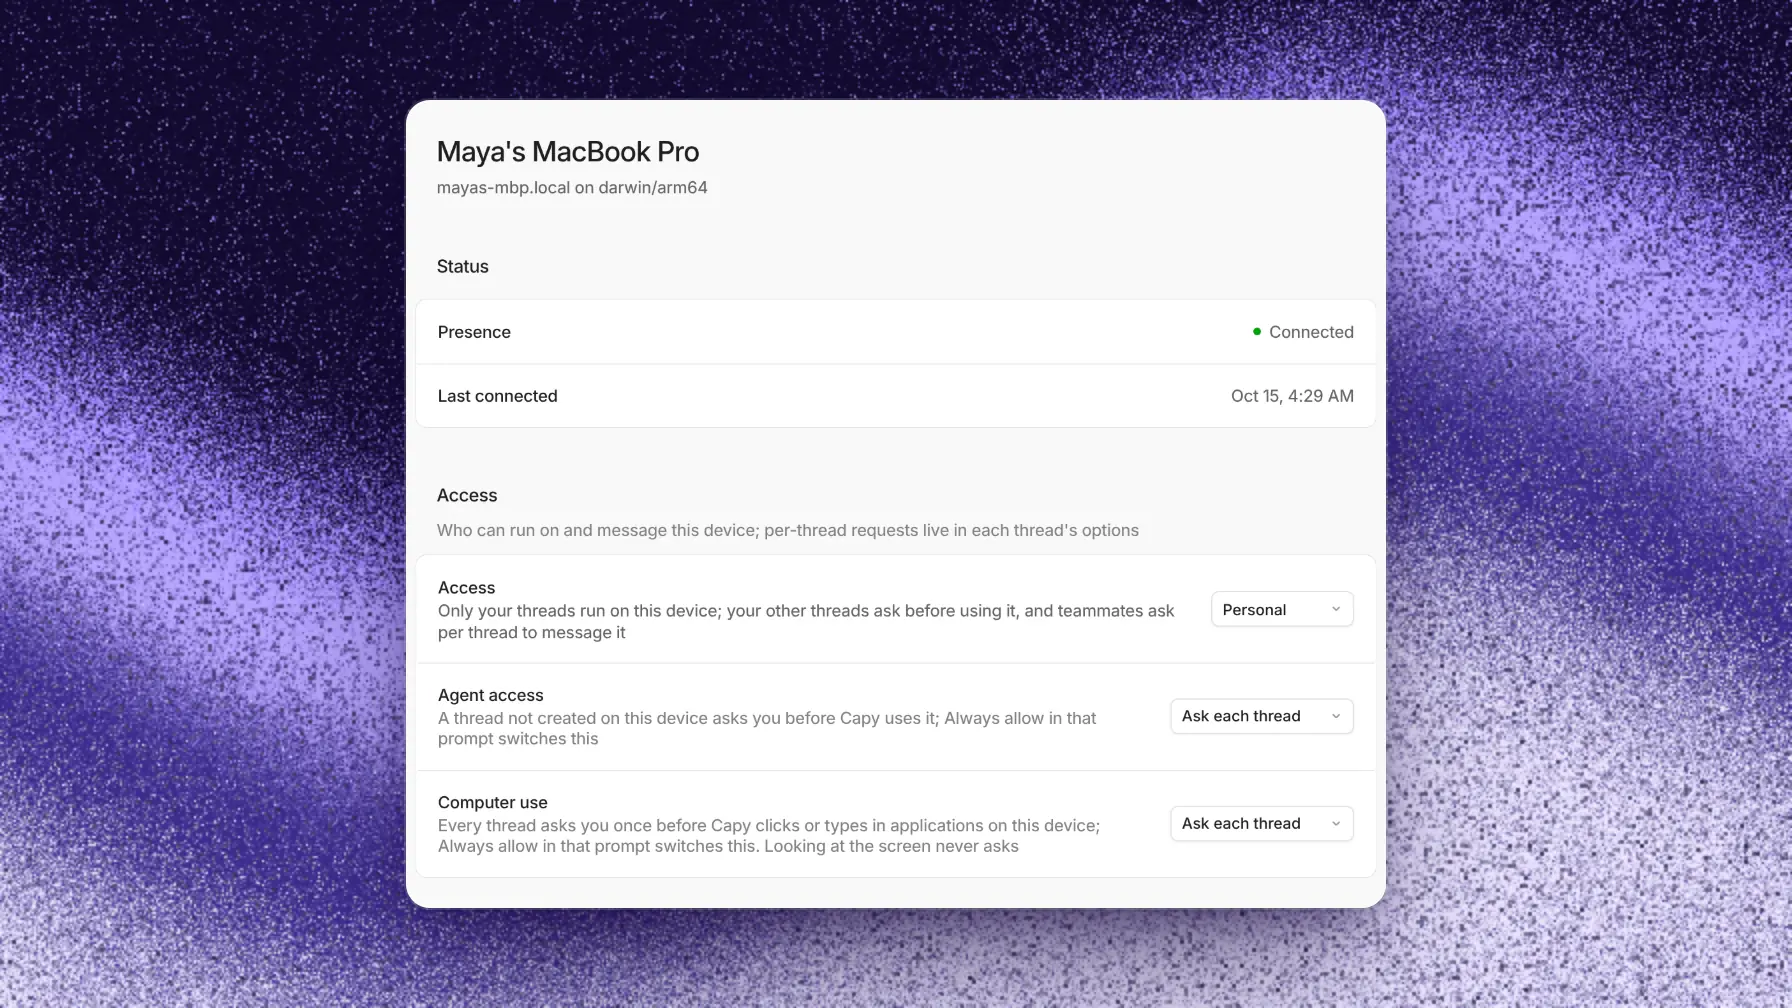
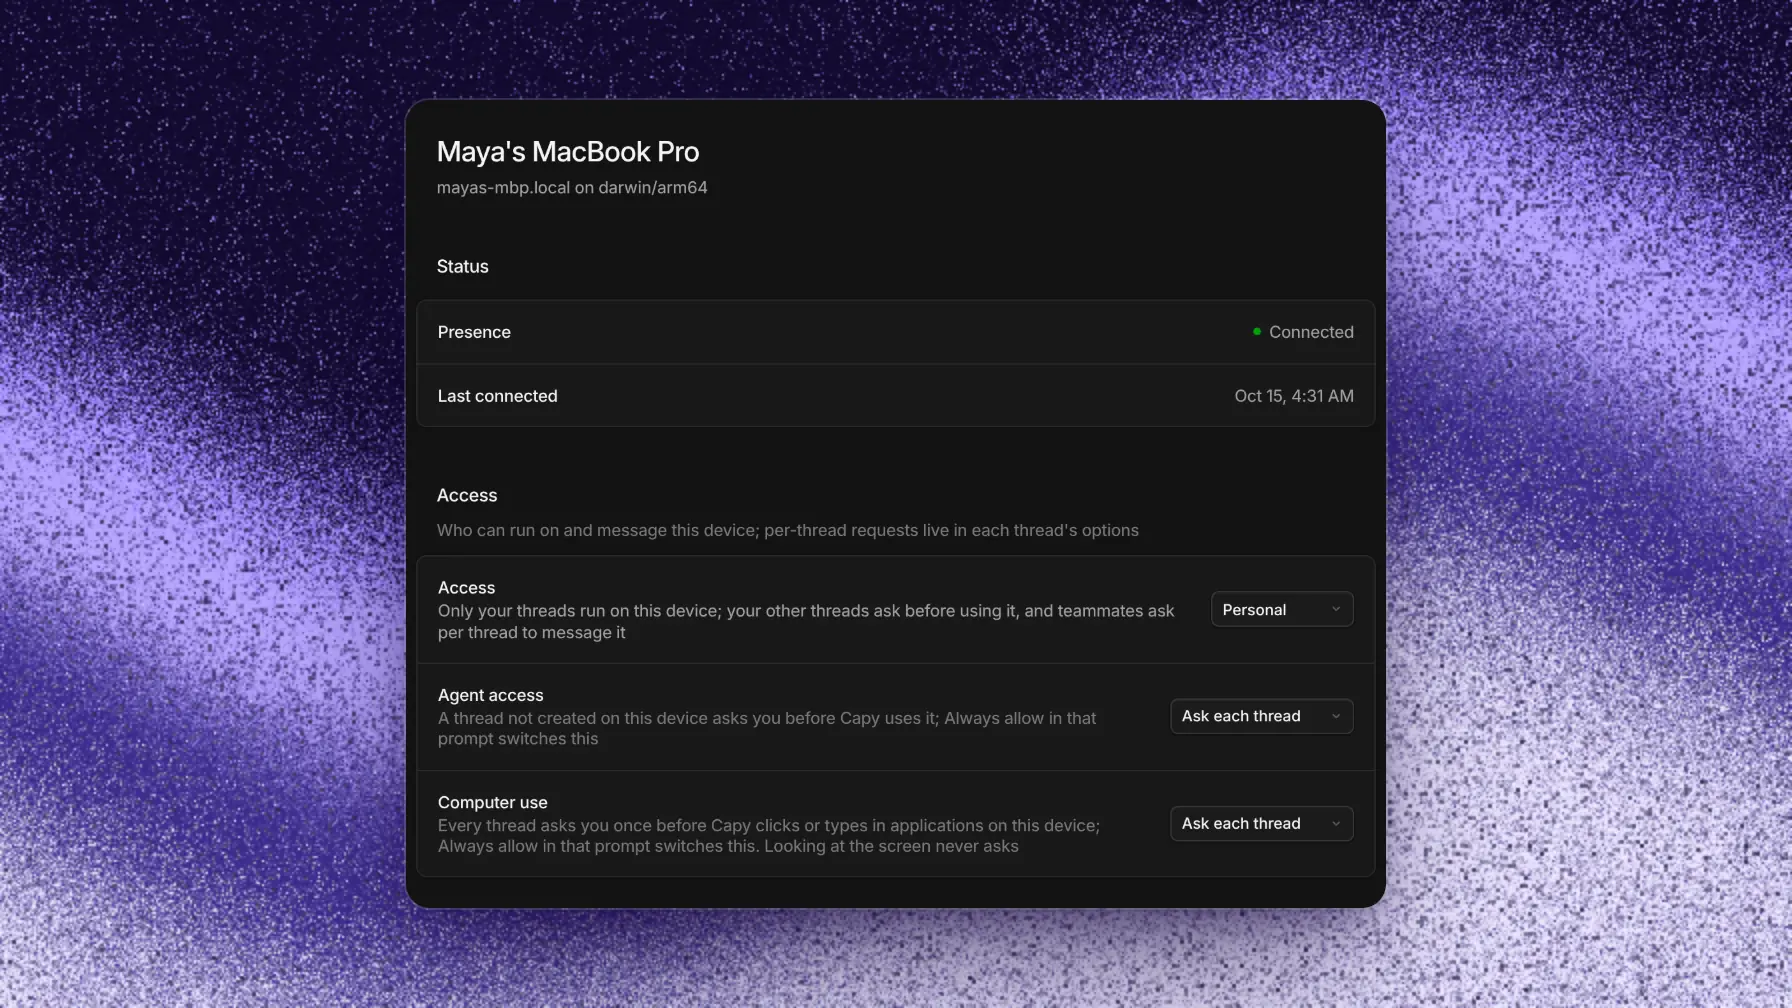
A device you pair with the desktop app starts as Personal. Only your threads run on it, and you approve or deny each request to message a thread there. Your threads that started elsewhere ask before they use it, unless Agent access is Always allow.
Settings → Devices controls device access. Shared lets your team run threads on the device, reach it from any thread, and message its threads. Organization API keys can then use the device too. Only you can change Access. Admins can see, rename, and revoke every paired device.
On your device, the agent reads and edits files and runs commands as you, under your local git identity, even when a teammate starts the thread. A linked folder sets where the agent starts, but it isn't a sandbox.
GitHub
Cloud machines hold no GitHub token, and git and gh work normally on them. Machines that run reviews can read but can't push. Threads on your device use the device's git credentials, while GitHub App actions, such as opening pull requests, run from Capy's cloud. See How Capy authenticates.
Capy's instructions tell it never to merge a pull request or turn on auto-merge unless you ask for that merge in the current conversation. AGENTS.md files and project rules can change how Capy works, except for three rules: no merging without your ask, no exposing or committing secrets, and no fabricating results.
GitHub App permissions
| Permission | Access | What Capy uses it for |
|---|---|---|
| Contents | Write | Clone, fetch, and push Capy's working branches |
| Pull requests | Write | Open and update pull requests, read reviews, and post review comments |
| Issues | Write | Post comments on a pull request's conversation, which GitHub handles as issue comments, and read issues you point Capy at |
| Checks | Read | Read CI results so a failing check wakes the thread |
| Commit statuses | Write | Post the optional capy/review status on reviewed commits |
| Actions | Write | Receive workflow run events for automations, and let the agent read CI logs and re-run jobs |
| Workflows | Write | Push commits that change files under .github/workflows, which GitHub allows only with this permission |
| Metadata | Read | List repositories, which GitHub requires for every app |
| Members | Read | Check that you're an organization admin when you link an installation |
| Email addresses | Read | Find the email to use as your commit author |
| GPG keys | Write | Add Capy's signing key to your account when you turn on signed commits |
| Deployments | Read | Granted, not used |
| Discussions | Write | Granted, not used |
GitHub doesn't let you install the app with fewer permissions. You choose which repositories the installation covers, and Capy can't see a repository outside it. For private repositories that Capy should only fetch, such as shared libraries your code depends on, an admin can install the optional Dependency reader app instead, from Settings → Integrations → GitHub. Capy never pushes or opens pull requests through it.
Secrets
Project environment variables are encrypted at rest. The agent sees each variable's name and whether it has a value, never the value. Secrets explains the scopes and how values reach a machine.
Capy doesn't scrub command output. Code the agent runs can read every variable on the machine. A command that prints a value puts it in the transcript, multiline values included.
Give the agent revocable credentials scoped to the job, such as a read-only production role. Put credentials that are yours alone in personal or thread variables. Capy doesn't connect to password managers.
Product analytics
Capy collects service usage data, such as features used and account activity, to run, improve, and support Capy and to send product and marketing email. It doesn't include your code, prompts, messages, files, or repository names.
Capy keeps this data in internal systems that only Capy staff use. Marketing emails include an unsubscribe link. The Privacy Policy covers this data, and the Subprocessors page lists the providers.
Desktop app telemetry
The desktop and web apps include no third-party analytics or session recording. They send Capy:
- Your threads, settings, and files.
- Error reports and performance data, such as error messages and page load times.
- Update checks. The desktop app installs updates when you quit.
- A paired device's open connection, so threads can run on it.
Crash dumps and log files stay on your computer unless you choose Export logs on the crash screen and send the file yourself. The support chat loads only when you open Contact us. It shares your name, email, and account and app details with the support tool.
Good to know
- An archived thread keeps all its data and can wake again. Delete it to remove the data.
- A thread started from a Slack channel, a Linear issue, or a GitHub comment is shared. A direct message with the Capy Slack app follows your default. In a private project, all of these threads stay limited to the project's people.
- On GitHub, what each person can do follows their own GitHub access, whatever their access in Capy.
- When an MCP server fails to start, the error hides the server's configured secret values of 8 characters or more, as exact matches only. A value in another form, such as base64 or with different line breaks, isn't hidden.