Members
Roles
Every organization member has one of three roles:
| Role | What they can do |
|---|---|
| Owner | Full control - billing, members, settings, integrations, projects |
| Admin | Manage members, projects, integrations, and settings |
| Member | Create and run threads, view projects they have access to |
An organization can have multiple owners. Transferring ownership is granting the owner role to another member and then revoking your own.
Invitations
Settings → Members manages invitations, roles, and domains. Any member can invite one or more email addresses. Invitees receive an email with a link to join.
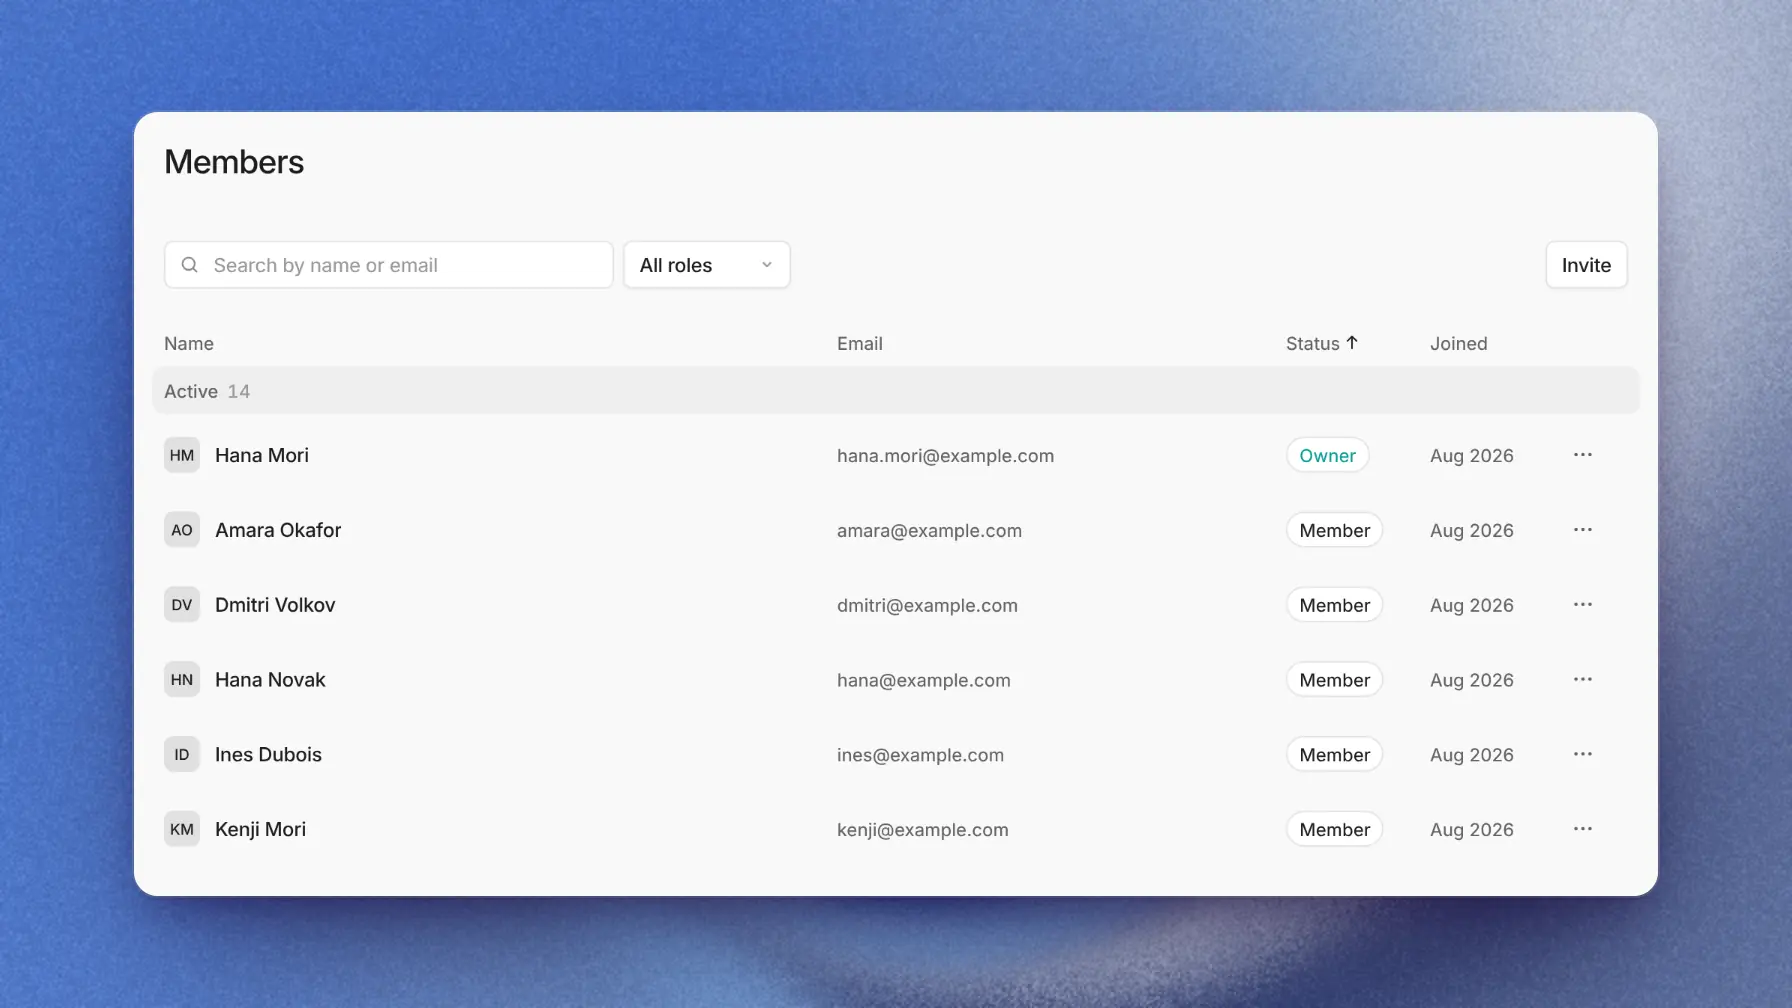
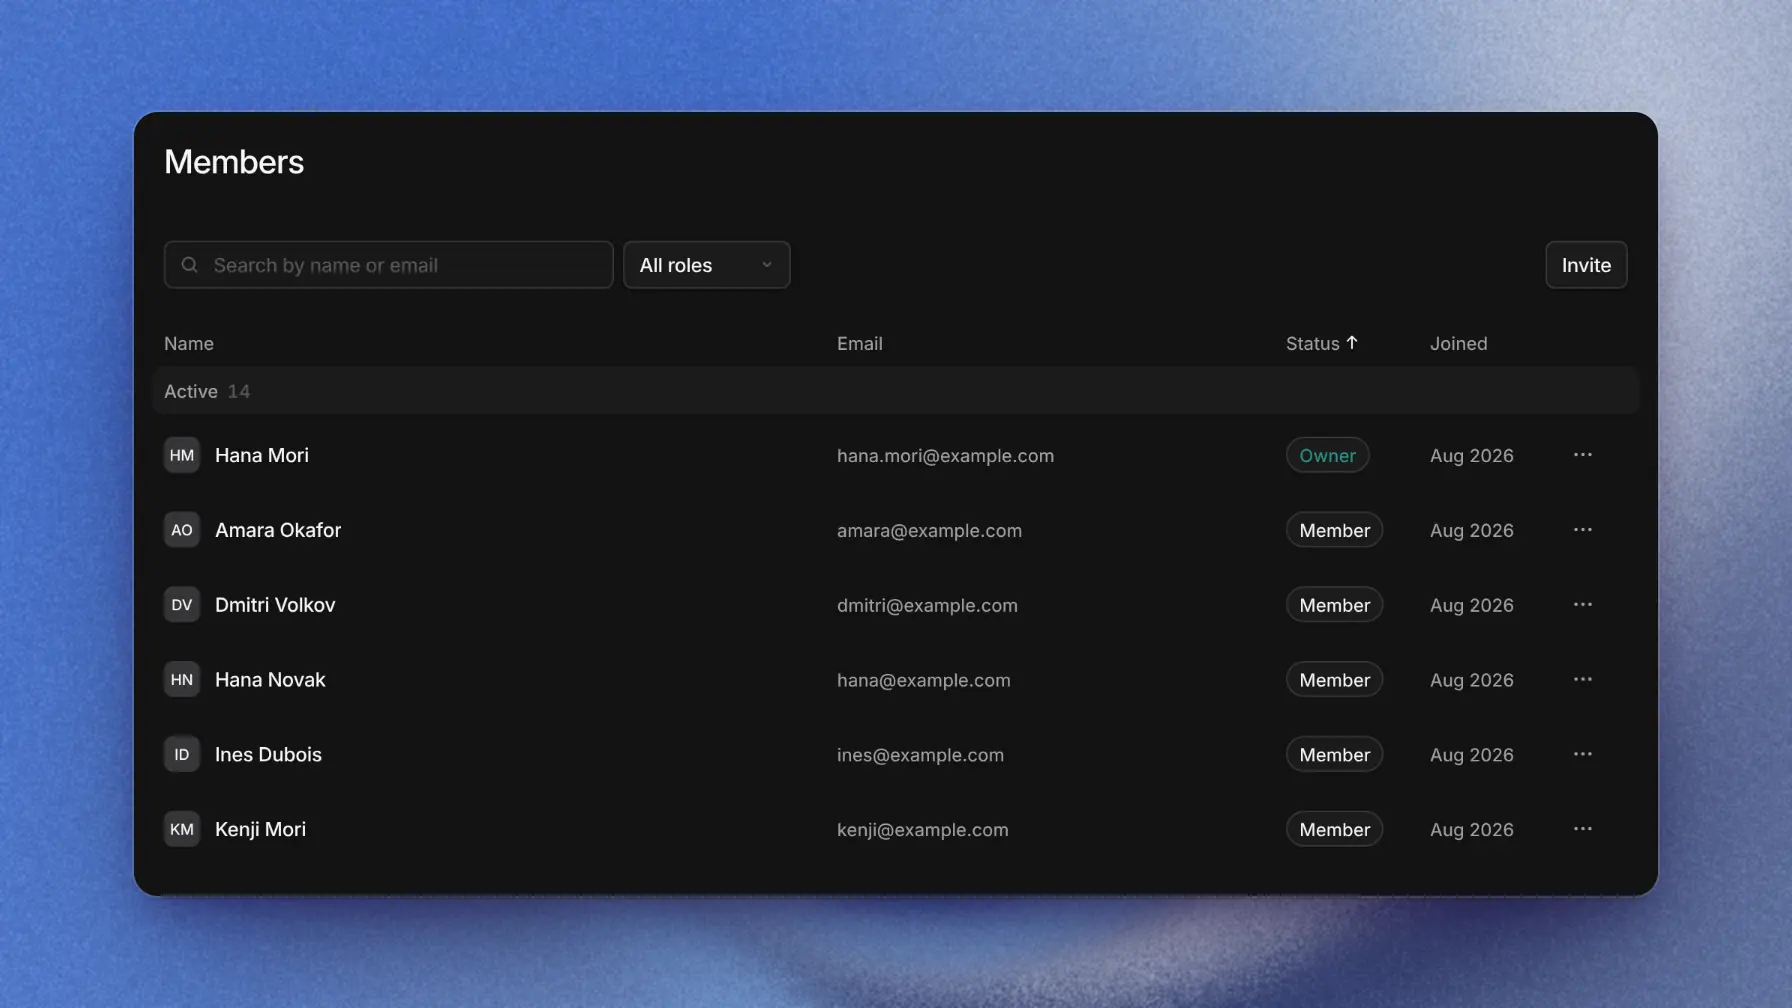
Every invitee joins as a member and can be promoted to admin after acceptance. Pending invitations appear in the members list. The inviter or an admin can revoke an invitation before acceptance.
Every plan includes unlimited members: inviting someone never creates a seat charge, and no invite is ever blocked over member count. The billing page labels a workspace Personal with zero or one active member and Team with more than one, but a second member still doesn't add a member fee. See pricing.
Join by domain
Admins can allow an email domain so anyone with a verified email on it can join without an invitation, in one click.
Adding a domain requires your own verified email to match it. Public email domains are rejected. People with a verified email on an allowed domain see the organization as joinable and join as members.
A domain isn't owned by one organization: several organizations can allow the same domain, and a joiner picks which to join. Removing the domain stops future joins; it doesn't remove existing members.
Managing members
From the members page, admins and owners can:
- Promote a member to admin or demote an admin to member.
- Remove someone from the organization.
Only owners can grant or revoke the owner role, including stepping down themselves. An organization always keeps at least one owner.
Leaving an organization isn't self-serve. Ask an admin to remove you.
Service users
A service user is a non-human principal for automations and API integrations: it acts as the explicit identity behind an API key or an automation's run-as identity, so unattended work never impersonates a person. Service users are not members: they take no invitations, and they carry their own roles and project access, plus optional subscription grants for seat-billed models.